Fairs 2026
Cybersecurity Summit Hessen – August 13th 2026 Marburg Lokschuppen
it-sa 2026 – October 27th to 29th 2026 Nuremberg
SMARTCITY Expo – November 3rd to 5th 2026 Barcelona
protekt – November 10th to 11th 2026 Leipzig
E-world energy & water – February 16th to 18th 2027 Essen
SWISS CYBER SECURITY DAYS – February 23th to 24th 2027 Bern
Hanover Fair – April 5th to 9th 2027 Hannover
Cybersecurity Summit – April 21th to 22th 2027 Hamburg
Security under control – March 2nd to 3rd Duisburg
AFCEA – May 25th to 26th 2027 Bonn
it-sa 2027 – October 2027 Nuremberg
August 2026

🔐 31,000 reasons to rethink the word „security“.
🇱🇮 Liechtenstein financial centre – safe?
Liechtenstein stands for stability, long-termism, regulation and asset protection. A combination that sounds attractive, especially in uncertain times.
But what does financial security actually mean today?
An extensive cyberattack has raised exactly this question anew: Data of around 31,000 legal entities were apparently illegally retrieved from the „register of beneficial owners“.
⚠️ Banks and bank customer data are not affected. There is also no evidence so far that data has been changed or deleted.
That’s important.
But it doesn’t make the incident unimportant.
After all, real asset protection today does not end with the vault, equity ratios or strict regulation. 🔒
🔴 Data protection is asset protection.
🔴 Cybersecurity is financial security.
🔴 And trust is a currency.
Perhaps we should therefore ask less:
👉 „Where is my wealth safe?“
And more often:
👉 „How comprehensively is what is associated with my assets protected?“
After all, the quality of a financial centre is not only shown by how well it manages assets.
But also by how well it protects trust. 🛡️

🛡️ Resilience becomes a duty! Progress is being made: The German government is planning the Resilience Fund. 👍
The German government is drawing consequences: A new „resilience fund“ is to better equip the German economy against drone attacks, power outages and cyberattacks on critical infrastructure. 🔌⚡
The initial situation is sobering: Many companies have so far underestimated external attack risks and invested too little in protective measures for their investments. Providers of cybersecurity solutions know this all too well, unfortunately.
This is exactly where the planned fund comes in – as a clever incentive mechanism that makes business and the state jointly responsible. 🤝
Particularly noteworthy: The energy industry itself has been calling for this step for a long time. The BDEW (Federal Association of Energy and Water Industries) puts it in a nutshell – resilience is a task for society as a whole.
💡What convinces me about the project:
✅ Coalition agrees on a multi-billion euro instrument
✅ Focus on protecting energy infrastructure – the neuralgic point of modern cybersecurity strategies
✅ Incentives instead of pure regulation – companies are empowered, not just obligated
However, it is also clear that responsibilities, financing and concrete design must now be clarified quickly. I know it’s difficult, but a good approach thrives on its implementation.
🎯How do you assess the initiative – is one fund enough, or do we need further regulatory steps for real cybersecurity resilience? 💬
July 2026

A government employee opens his mailbox in the morning. Everything seems normal. But his access data is already for sale on the darknet.
This is exactly the scenario that is currently occupying Great Britain. According to media reports, the login credentials of government officials were compromised and email accounts were the target of a large-scale cyberattack. Among others, employees of ministries, embassies and local governments are affected.
❗Access data to organizations in the critical infrastructure environment – including healthcare, energy supply and pharmaceutical suppliers – is also to be offered on the darknet.
Unfortunately, cyberattacks on the public sector are anything but an abstract threat. They are not only aimed at individual authorities, but also at trust in state institutions and the stability of critical services.
For government agencies and public institutions, this results in clear fields of action:
🔹 Consistent protection of digital identities and privileged access.
🔹 End-to-end multi-factor authentication and zero trust concepts.
🔹 Continuous monitoring of compromised credentials and rapid incident response.
🔹 Regular sensitization of all employees – because every account can become a gateway.
Cybersecurity is a central component of state resilience – how well prepared are public institutions in Germany for the increasingly imaginative cyberattacks?

🔴 What does cybersecurity have to do with environmental protection?
A look at the slides of a lecture on the topic of ‚International Relations‘ makes me think – here is the excerpt:
„Why are international environmental agreements difficult to achieve and often too weak?
•Liberalism I: Nationally, environmental protection goes hand in hand with the so-called prevention paradox. Prevention requires environmental protection measures before the environmental problem has occurred.
🔴 In advance, prevention is politically difficult to enforce because the problem is ➡️ not yet there Prevention policy is suspected of „causing panic“
🔴 In retrospect, successful prevention seems politically superfluous because the problem did not arise ➡️ Prevention policy is suspected of having been „superfluous“ (Prof. Dr. Bernhard Zangl, LMU)
When I read this, I discover parallels that make me very thoughtful: is prevention in the field of cybersecurity really always taken as seriously as it is necessary? Or is it perhaps more likely that some decision-makers are thinking that „panic is being made?“
And also the phenomenon that there is no problem with very good protection against cyberattacks: Can one or the other company possibly think that it has invested too much in security, that this is ultimately even superfluous? That you can take a little more time and invest better in other topics?
What is the prevention paradox in the cybersecurity sector in German companies and institutions?
June 2026

❗What the BSI warns about in particular – the 8 most common types of cyberattacks ❗
The most common ways to attack companies and institutions of all types and sizes are shown in the current BSI situation report on IT security in Germany 2025.
❗Ransomware ❗ Phishing ❗ Social Engineering ❗ DDoS Attacks ❗ Exploiting Unpatched Vulnerabilities ❗ Malware and BOTNETS ❗ APT ❗ Supply Chain Attacks
Ransomware attacks hit SMEs particularly often – according to the BSI, they account for around 80% of the reported cases. In 2025, 1,041 ransomware attacks were reported. Ransom demands have increased. There is also an interesting interview in the Handelsblatt (from 12/13/14 June) with two experts, Michael Sjøberg and Peter Skovbo, who explain how companies negotiate with cybercriminals. And what they recommend under the headline „The worst mistake is a CEO who asks: How do I pay?“.
What the BSI report also shows: The number of overload attacks (DDoS attacks) has increased by 25%, particularly affected: authorities, administrations, transport and logistics industry.
🛡️ And how do you protect yourself? How would you assess the cyber resilience in your company? How do you detect attacks in time? Do you use honeypots, how do you counter the human risk? … ? We are happy to answer any questions you may have.

🔐 “We’re not affected by NIS2 at all,” thought the supplier. That is, until their most important customer sent a comprehensive cybersecurity questionnaire and made new security requirements a contractual condition.
👟 One of the most well-known supply chain attacks was the attack in February on a partner of the sporting goods manufacturer Adidas, in which 815,000 data records were allegedly stolen.
📈 The reality: NIS2 no longer only affects companies directly subject to regulation. Because regulated companies must assess risks along their supply chains, suppliers, service providers, and medium-sized businesses are also increasingly coming into focus.
⚠️ Cyberattacks today frequently occur via the supply chain. Therefore, topics such as patch management, multi-factor authentication, backup strategies, access management, and documented security processes are increasingly becoming business-critical factors.
🤝 Cybersecurity is thus evolving from a purely IT issue to a competitive and trust factor. Companies that document their security measures transparently and communicate them realistically strengthen customer relationships and reduce liability risks.
💡 The most important message: While NIS2 may not directly regulate all companies, its impact on supply chains and business relationships affects virtually every business.
Mai 2026
❓Which small or medium-sized enterprise (SME) has half a million euros set aside for a cyberattack these days?
The reality is: SMEs remain the primary targets of cybercriminals. 💻⚠️
And according to recent statements by Interior Minister Dobrindt, Germany ranks third internationally among the most attacked countries – right behind the USA and Canada. 🇩🇪
While not all affected companies pay ransoms, where payments have been made and cases are statistically recorded, the average sum was around 500,000 euros. 💸
The consequences, however, extend far beyond individual companies:
📉 Production losses
📉 Sabotage
📉 Extortion
📉 Data loss
The annual economic damage caused by cyberattacks is now estimated at over 200 billion euros. An enormous burden on the entire economy.
🛡️ That’s why active cyber defense is to be significantly expanded. As early as May, the German government plans to grant new powers to security agencies like the Federal Criminal Police Office (BKA). The goal is to detect criminal networks early, analyze their structures, identify perpetrators, and take targeted action against international cybercrime.
Cybersecurity is economic protection. Business protection. Future protection. 🔐

IWF warns financial world
💻⚠️ Imagine: A single AI-powered cyberattack suddenly cripples banks, payment systems, and critical infrastructure. What long sounded like science fiction is now becoming a real concern for the financial world.
🌍🏦 The International Monetary Fund (IMF) is issuing a stark warning about a new generation of AI-driven cyberattacks using the „Mythos“ model. Particularly alarming: Security vulnerabilities could be automatically detected and exploited – even without in-depth expert knowledge.
🤖🔓 The IMF is already speaking of potential „macro-financial shocks“ and a dangerous chain reaction for the global financial system. 🚨📉
Cybersecurity is therefore no longer just an IT issue, but a central question for economic stability. 🔐🌐
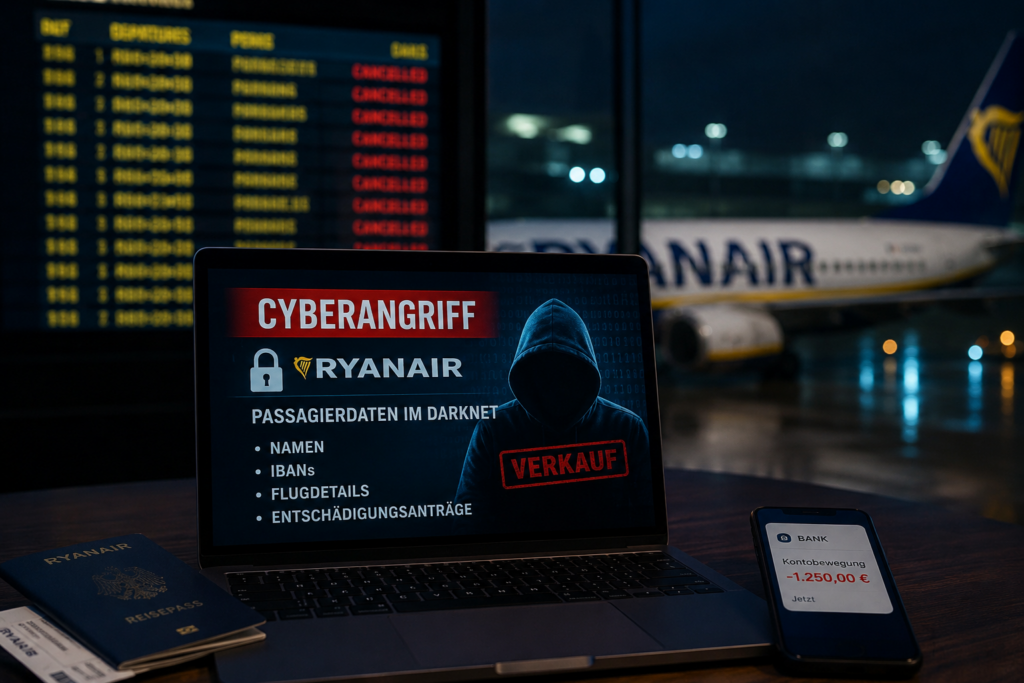
The aviation industrie is increasingly becoming a target for cybercriminals
First strikes. Then closed airports. Now passenger data on the dark web. 😳
The suspected hacking attack on Ryanair shows once again: The biggest threat to airlines doesn’t just come from the air – it comes from the internet. 💻⚠️
Reports indicate that sensitive passenger data has been compromised:
📌 Names
📌 IBANs & SWIFT codes
📌 Flight details
📌 Compensation claims
Particularly critical: The data could be used for phishing, fraud, and identity theft.
🚨 And with every incident, the question grows: How secure is our data really? 🔐
April 2026
Hanover Fair 2026
Amidst innovations, machines, and future technologies – and suddenly the crucial question arises: How secure is it all, really? 🔐 That’s exactly what we should be talking about.
I’ll be at Hannover Messe 2026 – and I’m looking forward to connecting with you there! The trade fair is one of the most important meeting places for product innovations and new technologies. And one thing is clear: Cybersecurity is absolutely essential these days. 💻⚠️
📍 I’ll be in Hannover on Wednesday, April 22nd, and Thursday, April 23rd. 📞 Let’s have a spontaneous or scheduled chat – just send an email with a suggested time to m.betz@bcm5.de
I’m looking forward to engaging conversations, new perspectives, and real-world insights! 👉 Who else will be there and interested in discussing cybersecurity?
What if?
Drones fly undetected over a country. False corruption allegations spread virally and influence elections. A state creates artificial islands to secure power and resources… Sounds like breaking news – but it’s a scenario.
👉 Welcome to „Zero Day.“
On Monday, April 20, 2026, „Locked Shields,“ one of the world’s largest cyber defense exercises, began:
🌍 45 countries
👥 4,000 experts
🎯 One goal: Protecting critical infrastructure from highly complex attacks. In the „Blue Team,“ countries including Germany, Austria, Switzerland, and Luxembourg jointly defend systems such as power plants and air defenses against a highly specialized „Red Team.“
💡 The reality behind it: Cyberattacks have changed. No longer just simple DDoS attacks – but AI-powered attacks, fast, precise, and daily.
➡️ The answer? Defense is also becoming more intelligent: more AI, more collaboration, more innovation.
Cybersecurity is no longer just an IT issue – it’s a central pillar of our security.
🚨 Following cyberattacks on critical infrastructure in the US: Important warning for operators in Germany as well 🚨
According to recent reports from the US, hacker groups with suspected links to Iran are carrying out targeted cyberattacks on critical infrastructure. Industrial facilities accessible via the internet are particularly affected – including government, water supply, and energy sector facilities. ⚡💧🏭
The attacks aim to manipulate user interfaces and display false data. This can lead to significant operational disruptions and financial losses. The true extent of the attacks is currently unclear. ⚠️💻
Furthermore, recent incidents – such as an attack on the Director of the FBI – demonstrate the increasing professionalism and targeted nature of such actors. 🎯
👉 What does this mean for Germany?
These developments underscore the urgent need to further enhance the cybersecurity of critical infrastructure in Germany as well.
🔐 Recommendations:
– Review and secure internet-exposed systems
– Strict network segmentation and access controls
– Regular updates and patch management
– Raising employee awareness of cyber risks
– Preparation for emergency and response scenarios
💡 Conclusion:
Cyberattacks on critical infrastructure are already a reality and are evolving rapidly. Now is the time to review and strategically strengthen protective measures.
March 2026
🚨 Cyberattack on high-ranking former intelligence official – a warning for us all!
In mid-March 2026, it was revealed that Arndt Freytag von Loringhoven, former Vice President of the BND (Federal Intelligence Service) and NATO diplomat, had been the victim of a targeted cyberattack.
👉 He was tricked into revealing his PIN to a supposed support team via a deceptively authentic phishing message.
👉 The result: access to sensitive personal data.
👉 Similar attacks were also directed against government officials, military personnel, and journalists.
Investigators suspect a state-sponsored background – evidence points to Russian espionage. This has not been officially confirmed, but the case has been classified as „security-relevant.“
💡 The most important takeaway:
If even experienced security experts can fall victim, it can happen to anyone.
🛡️ Specific precautionary recommendations:
✅ Do not share sensitive data. Support will never ask for PINs, passwords, or codes.
✅ If in doubt, stop. If in doubt, always contact the official channel directly – do not reply via chat.
✅ Activate two-factor authentication (2FA). An additional layer of protection can be crucial.
✅ Learn to recognize phishing. Pay attention to pressure („act immediately!“), unusual requests, or slight variations in the sender’s address.
✅ Keep devices and apps up to date. Updates close known security gaps.
✅ Promote awareness within the team. Cybersecurity is not an IT task – it’s a leadership responsibility.
⚠️ My conclusion:
Cyberattacks are becoming more targeted, personalized, and convincing. Trust is becoming the biggest attack surface.

🚀 Good News: More Cybersecurity for Business!
In times filled with negative headlines – from economic downturn to layoffs – this development sends a strong positive signal:
💡The German Federal Government has adopted a new National Economic Security Strategy.
The goal:
🔐 Better protect companies against espionage, sabotage, and cyberattacks
🔗 Make supply chains and innovations more resilient
🛡️ Establish a high, shared level of cybersecurity
Particularly important:
👉 Strengthening protection against hacker attacks (e.g., through NIS-2)
👉 Improved cooperation between the government and the private sector
👉 Focus on SMEs, which often lack their own security structures
This strategy builds on the National Security Strategy 2023 and is a crucial step towards greater economic security and future viability.
February 2026
😾 Baden-Württemberg again: Following the attack on the state’s marketing campaign, „The Länd“ (as we reported), the Schorndorf children’s project „Forschungsfabrik“ has now been affected. 😾
Around 20,000 people are believed to have been affected by the cyberattack – email addresses, passwords, and location data were apparently stolen (see report).
❓ The crucial question is: How can organizations effectively protect themselves – and prevent incidents of this kind? ❓
Cybersecurity doesn’t begin in an emergency, but with proactive prevention. Now is the right time to act.
We support you with suitable security solutions – reliable, field-tested, and entirely made and hosted in Germany.
January 2026
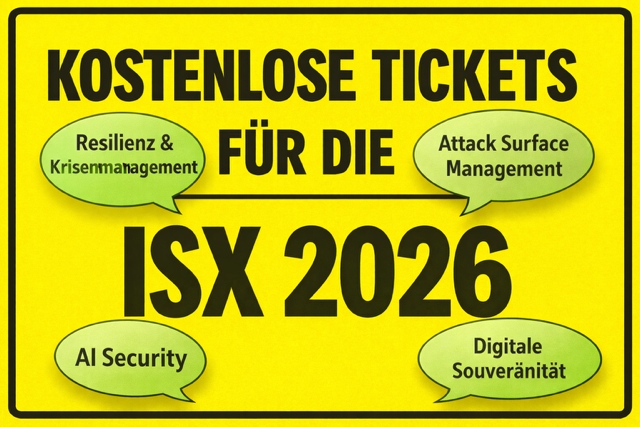
‼️ Free tickets for the ISX IT Security Conference in June 2026 in Frankfurt, Munich, Hamburg and Düsseldorf are available until January 31st 😄
In June, the ISX IT Security Conference will once again offer a mix of expert presentations and practical insights on highly topical cybersecurity issues, with ample opportunity for professional exchange. The target audience includes managers and service providers focused on IT security and cloud security, data security/data protection, IT consulting and integration, and (managed) security services.
Excerpt from the program:
RESILIENCE & CRISIS MANAGEMENT
Emergency Management • Cyber Incident Simulation • Business Continuity Plan • Crisis Communication • Human Resilience • Focus on Compliance: NIS2 and DORA • Focus on Supply Chain: Supply Chain Security & Vendor Risk Management
ATTACK SURFACE MANAGEMENT
Hacker Tools • Insider Risk Management • Hybrid Attack Scenarios • Prioritization of Security Measures • Microsegmentation • Managed Security Services
DIGITAL SOVEREIGNTY
Selection, Availability, Autonomy • Sovereign Security • Digital Sovereignty & Hyperscalers in Cybersecurity: Opportunities and Risks • Security Solutions from Europe/Germany
AI SECURITY
Attack Vectors • Manipulation of AI Agents • Cloud and Data Strategies for AI • Risk Scores, Firewall and Security Concepts • AI Guidelines • Technical Safeguards • AI-Powered Awareness Programs
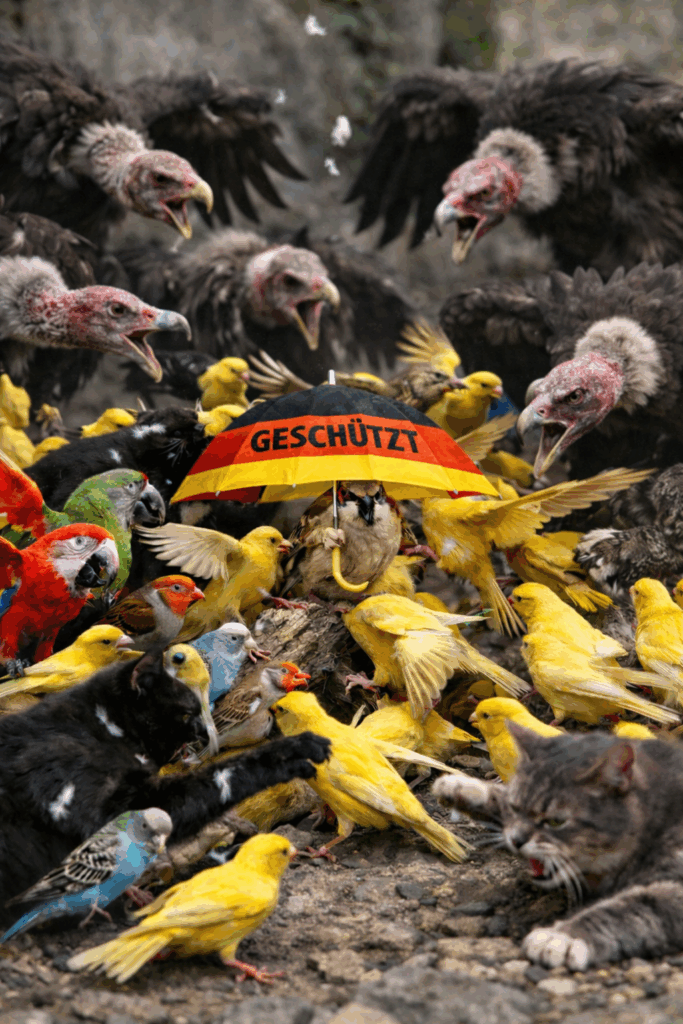
‼️2026 – The cyber threat landscape continues to escalate ‼️
AI-powered attacks, automated exploit chains, and highly professional cybercrime groups are massively increasing the speed, reach, and impact of attacks. Modern ransomware operates in a modular, lateral, and data-driven manner – focusing on exfiltration, persistence, and targeted extortion.
The figures for the end of 2025 are alarming: Since 2020, the number of successful cyberattacks has tripled, with an increase of 44.5% in 2025 alone (see press releases). Reported attacks include ransomware, data theft, supply chain compromises, unauthorized access, as well as AI-powered phishing and deepfakes that bypass traditional security mechanisms.
Critical infrastructure (KRITIS) is no longer the only sector affected. Attacks affect companies of all sizes and sectors – from industry and trade to SMEs and craft businesses. Hybrid IT, legacy systems, and a lack of transparency in the supply chain increase the attack surface.
With NIS-2, cybersecurity definitively becomes a management responsibility.
Resilient zero-trust architectures, continuous monitoring, incident response capabilities, and measurable security governance are required. Modern attacks no longer target individual systems but entire IT and OT infrastructures. At the same time, phishing campaigns and deepfakes are reaching a new level of sophistication through the use of artificial intelligence – traditional detection mechanisms are increasingly reaching their limits.
‼️ Cybersecurity is no longer an IT project – it’s a strategic resilience issue. ‼️
——-
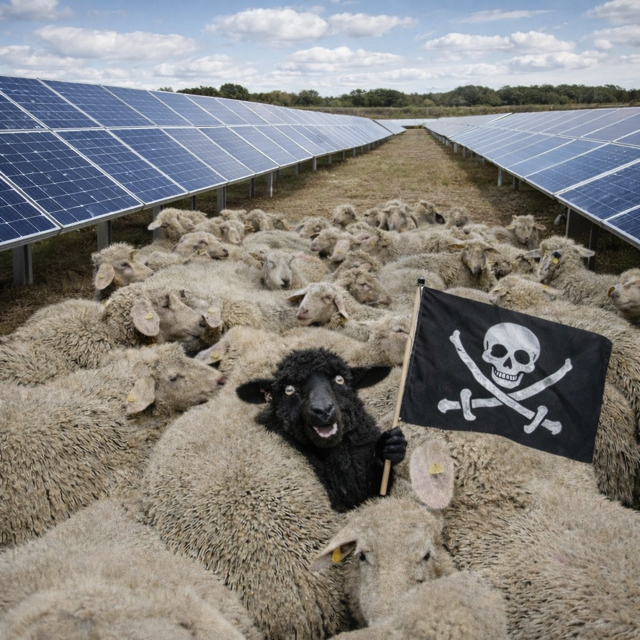
❓Are you sure that only reputable companies are using your solar parks?
More and more solar parks are supplying the necessary energy and playing a key role in Germany’s energy transition. This rapidly growing importance of photovoltaics simultaneously requires a greater focus on comprehensive security concepts. The rapid expansion significantly increases the need for action on the part of grid operators and municipalities.
With the increasing grid relevance of solar parks, the demands on their IT and OT security are rising. Many photovoltaic systems now perform functions that place them within the context of critical infrastructure.
The ongoing digitalization – for example, through networked inverters, remote maintenance, and monitoring systems – simultaneously increases the attack surface. Common vulnerabilities include unsecured remote access, a lack of separation between IT and OT, and outdated firmware.
The German Federal Office for Information Security (BSI) regularly warns of cyber risks in the energy supply sector. For operators and municipal utilities, this means that cybersecurity must be continuously and systematically integrated into operations
———
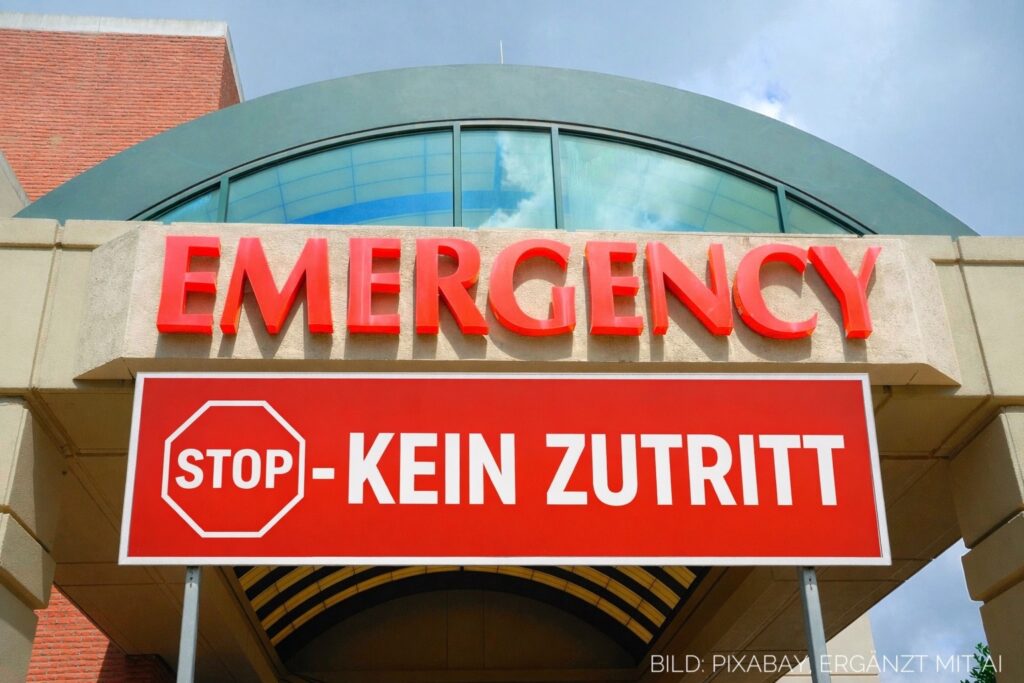
😾 Ruthless! No access for emergencies, no electricity in the freezing winter…
⚠️ Attacks on critical infrastructure affect innocent people.
Like the recent power outage in Berlin or the cyberattack on the Roth district hospital – the emergency room had to be closed!
People are left in distress, with no support – THAT is inhumane. Customers can hardly protect themselves in these and many other situations. The responsibility lies with the operators.
———————
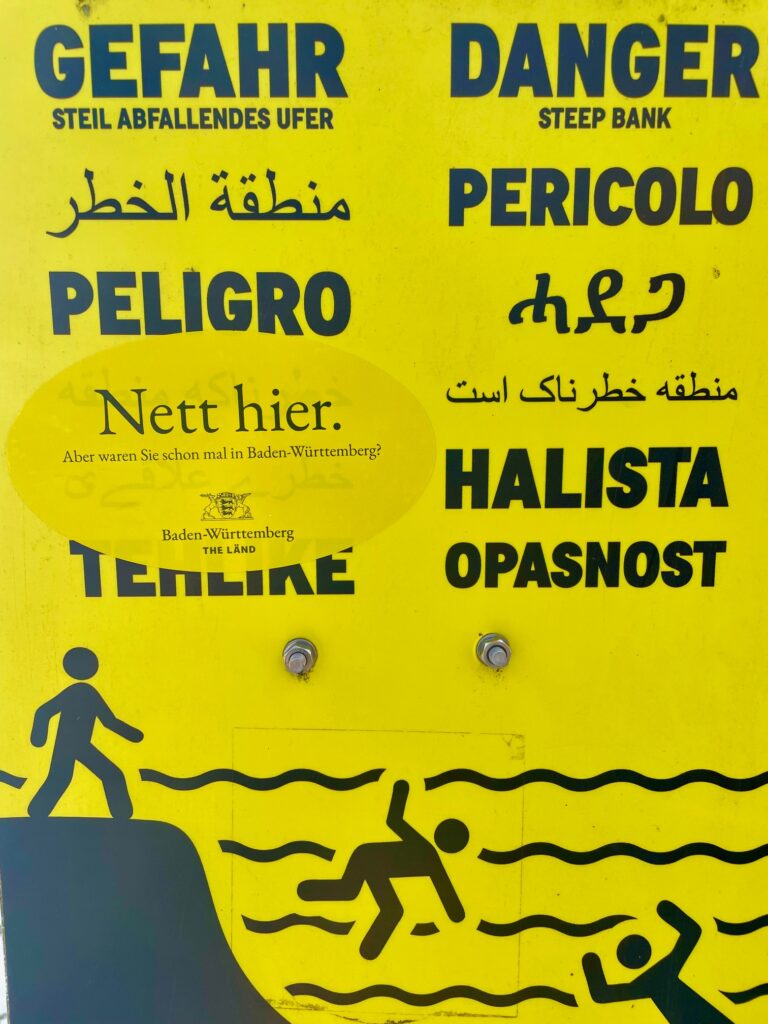
🔐 Embarrassing – Cyberattack on State Shop 🙀
The recent incident at the beginning of the year – a cyberattack on ‘The Länd’ – once again demonstrates that security vulnerabilities can compromise sensitive customer data. The online shop of the Baden-Württemberg state marketing campaign was attacked – and this was only discovered through customer reports.
👉 Shop operators also have a responsibility: IT security, regular updates, and preventative checks are not optional extras, but a legally binding obligation to their customers.
‼️ Data protection begins with prevention. Act now.
———————
🎆 Good vibes for 2026 – we wish all IT security professionals the best!
🔐 Greater awareness of cyber threats
🛡️ A sustainably high level of security awareness
🚨 Early and successful detection of attacks
👉 Use the start of the year to review your security strategy:
Are your awareness, detection, and response capabilities truly up to date with the current threat level?
💬 Let’s talk – about practical IT security that is not only compliant but also effective in a real-world scenario.
Interested? Please send us an email to m.betz@bcm5.de.